API Policies
The API Policies page lists the account's API policies. An API policy grants access to one Fluency API resource (such as data, search, collector, or user) with a set of privileges: read, create, update, delete, or all of them. API policies are given to users and tokens through roles, and can also be attached to an API token directly.
Menu path: Admin console → RBAC → API Policies · URL path: /v2/admin/api-policies
Task guide: Managing Roles: what each role can do.
Page Layout
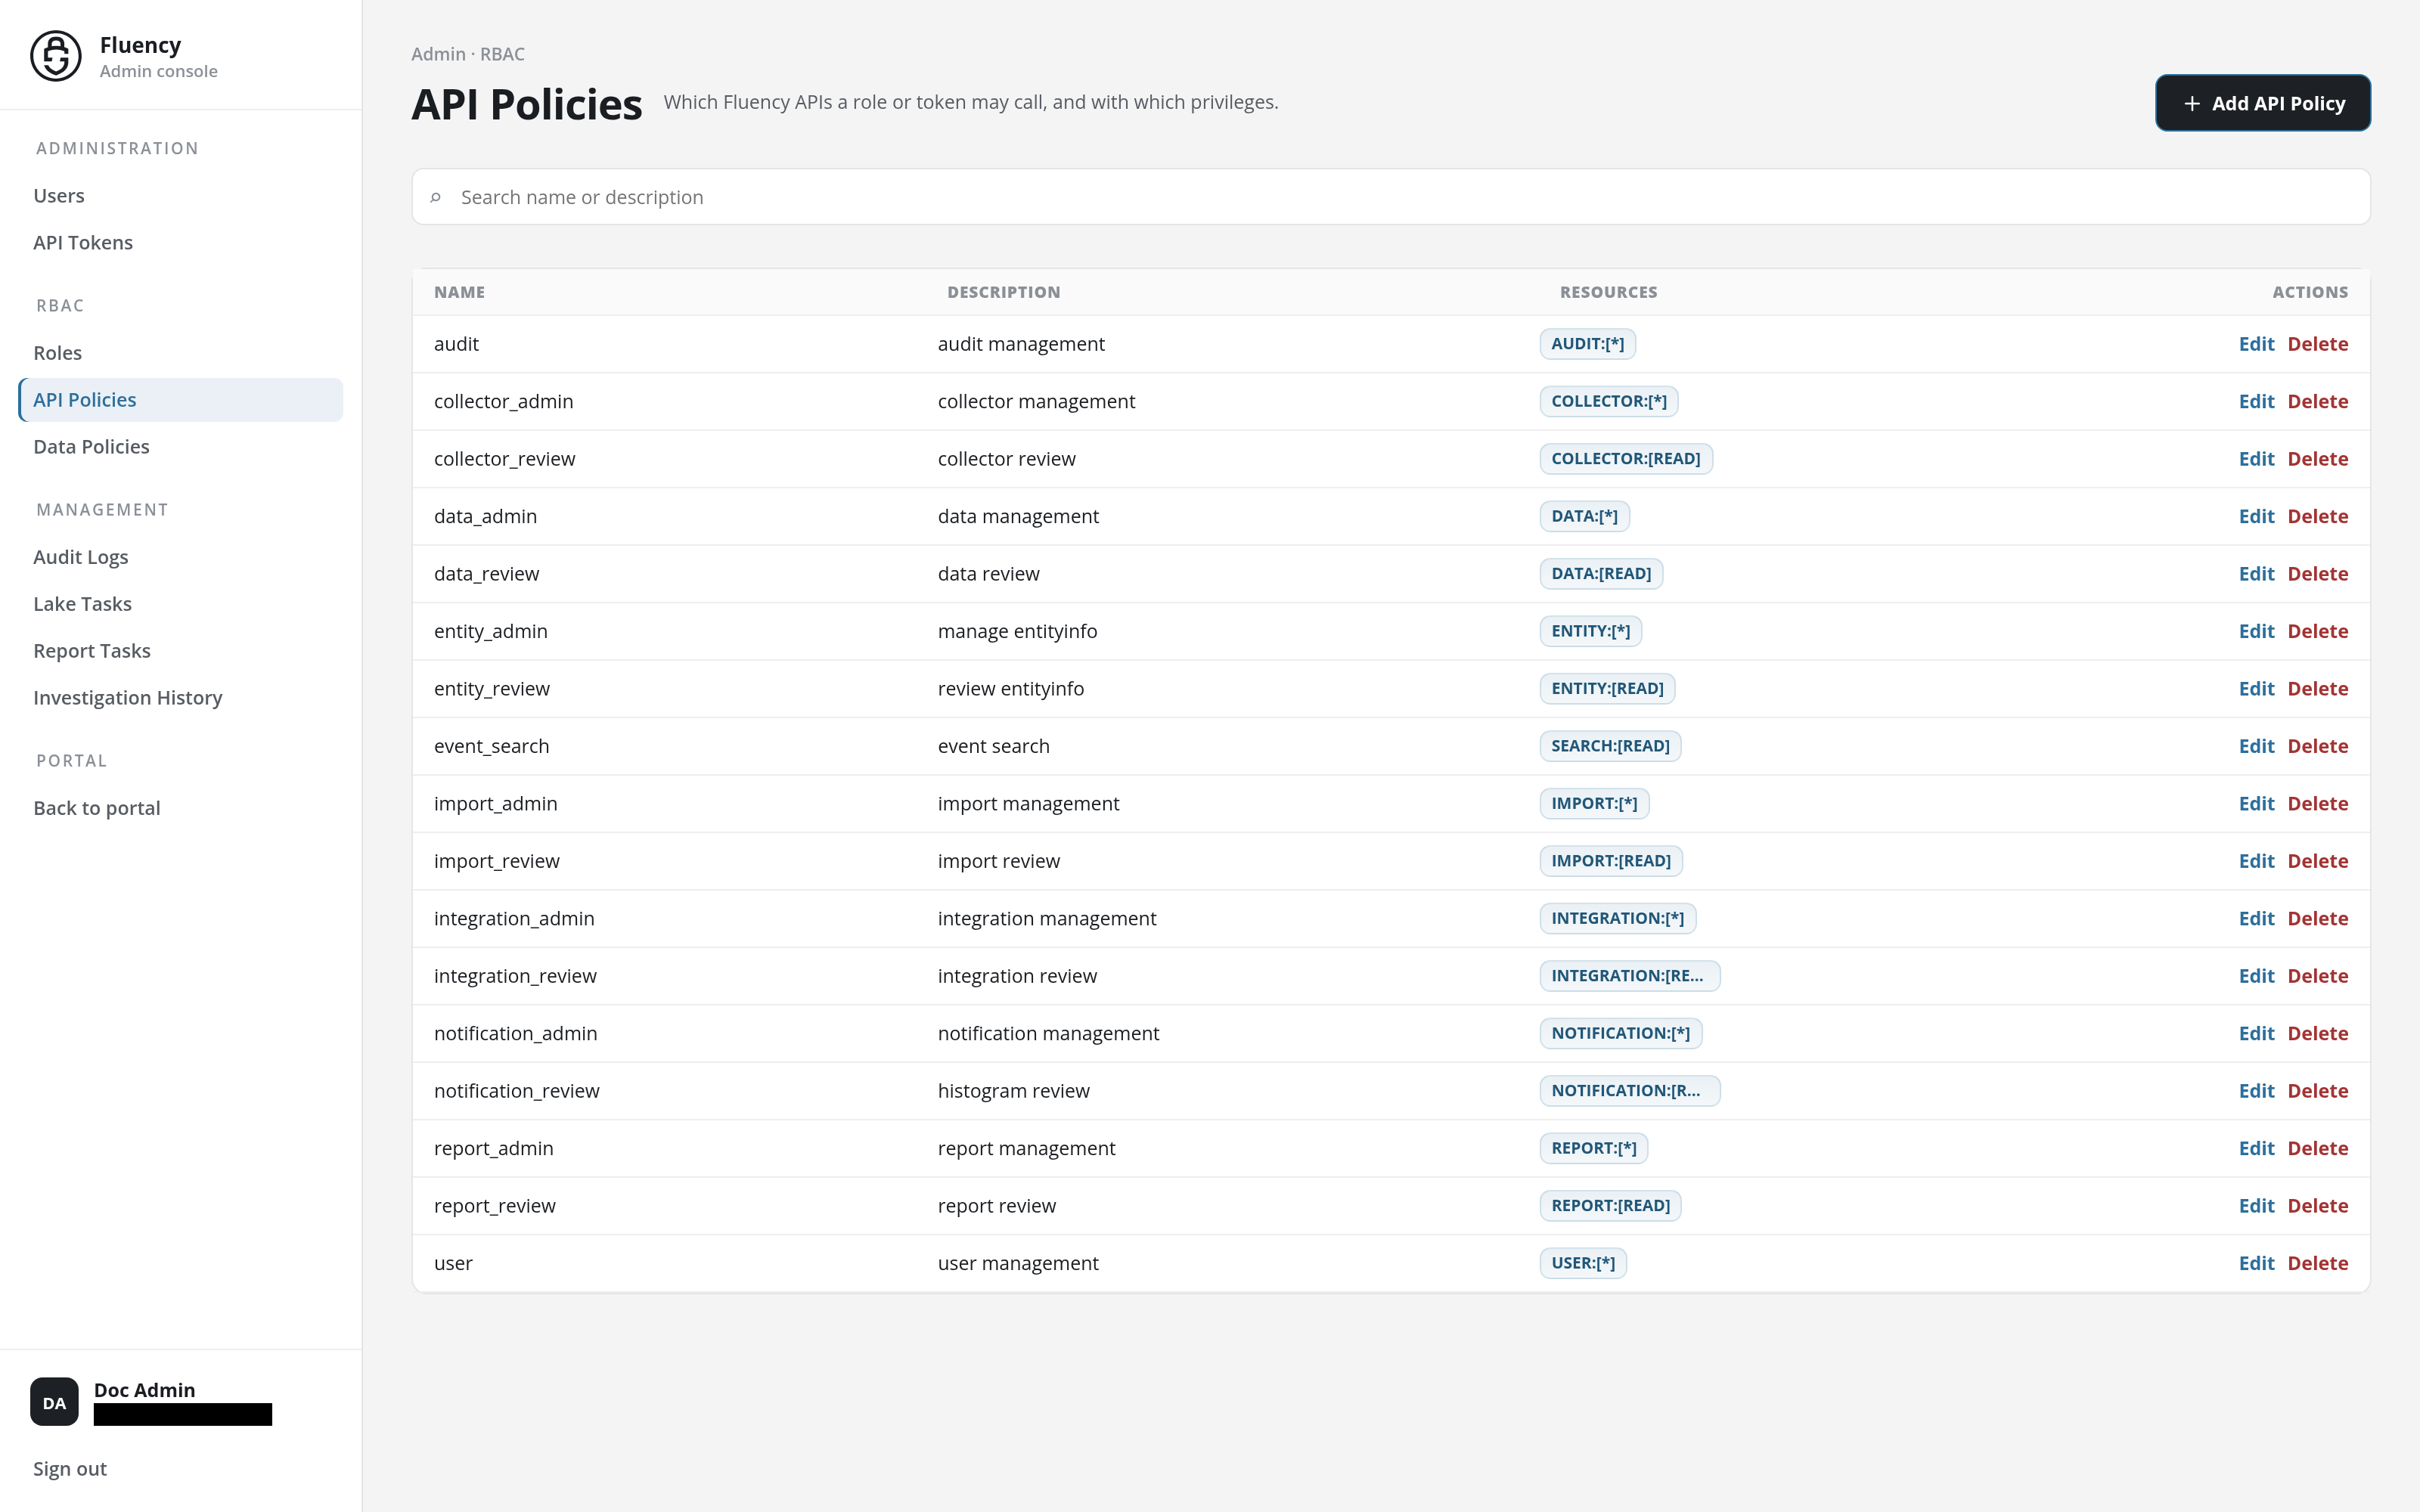
The page sits in the Admin console, with API Policies highlighted under RBAC in the side navigation.
- Header: the breadcrumb Admin · RBAC, the title API Policies with the subtitle Which Fluency APIs a role or token may call, and with which privileges., and the + Add API Policy button on the right.
- Search field: a full-width field with the placeholder Search name or description.
- Policies table: one row per API policy.
Search
Type in the Search name or description field to narrow the table to the policies whose name or description matches.
Policies Table
The table has four columns:
- Name: the policy's name, such as
collector_admin. - Description: the policy's description, such as collector management.
- Resources: a chip reading
RESOURCE:[PRIVILEGES]: the API resource the policy covers and the privileges it grants on it.COLLECTOR:[*]grants every privilege on the collector API;COLLECTOR:[READ]grants read access only. A chip too long for the column is cut short with an ellipsis. - Actions: Edit opens the policy in the Update API Policy dialog; Delete removes the policy (see Delete an API Policy).
Most of the policies in the example above come in pairs: an _admin policy that grants [*] on its resource and a _review policy that grants [READ].
| Policy | Resources |
|---|---|
audit | AUDIT:[*] |
collector_admin / collector_review | COLLECTOR:[*] / COLLECTOR:[READ] |
data_admin / data_review | DATA:[*] / DATA:[READ] |
entity_admin / entity_review | ENTITY:[*] / ENTITY:[READ] |
event_search | SEARCH:[READ] |
import_admin / import_review | IMPORT:[*] / IMPORT:[READ] |
integration_admin / integration_review | INTEGRATION:[*] / INTEGRATION:[READ] |
notification_admin / notification_review | NOTIFICATION:[*] / NOTIFICATION:[READ] |
report_admin / report_review | REPORT:[*] / REPORT:[READ] |
user | USER:[*] |
event_search (SEARCH:[READ]) on its own does not let a role run a KQL Search or a Datalake Search: reading and searching the data needs data_review (DATA:[READ]) or data_admin. See Roles → What a Role's Policies Allow.
Add API Policy
Click + Add API Policy to open the Add API Policy dialog. It has four fields:
- Name (required): the policy's name.
- Description: optional free text.
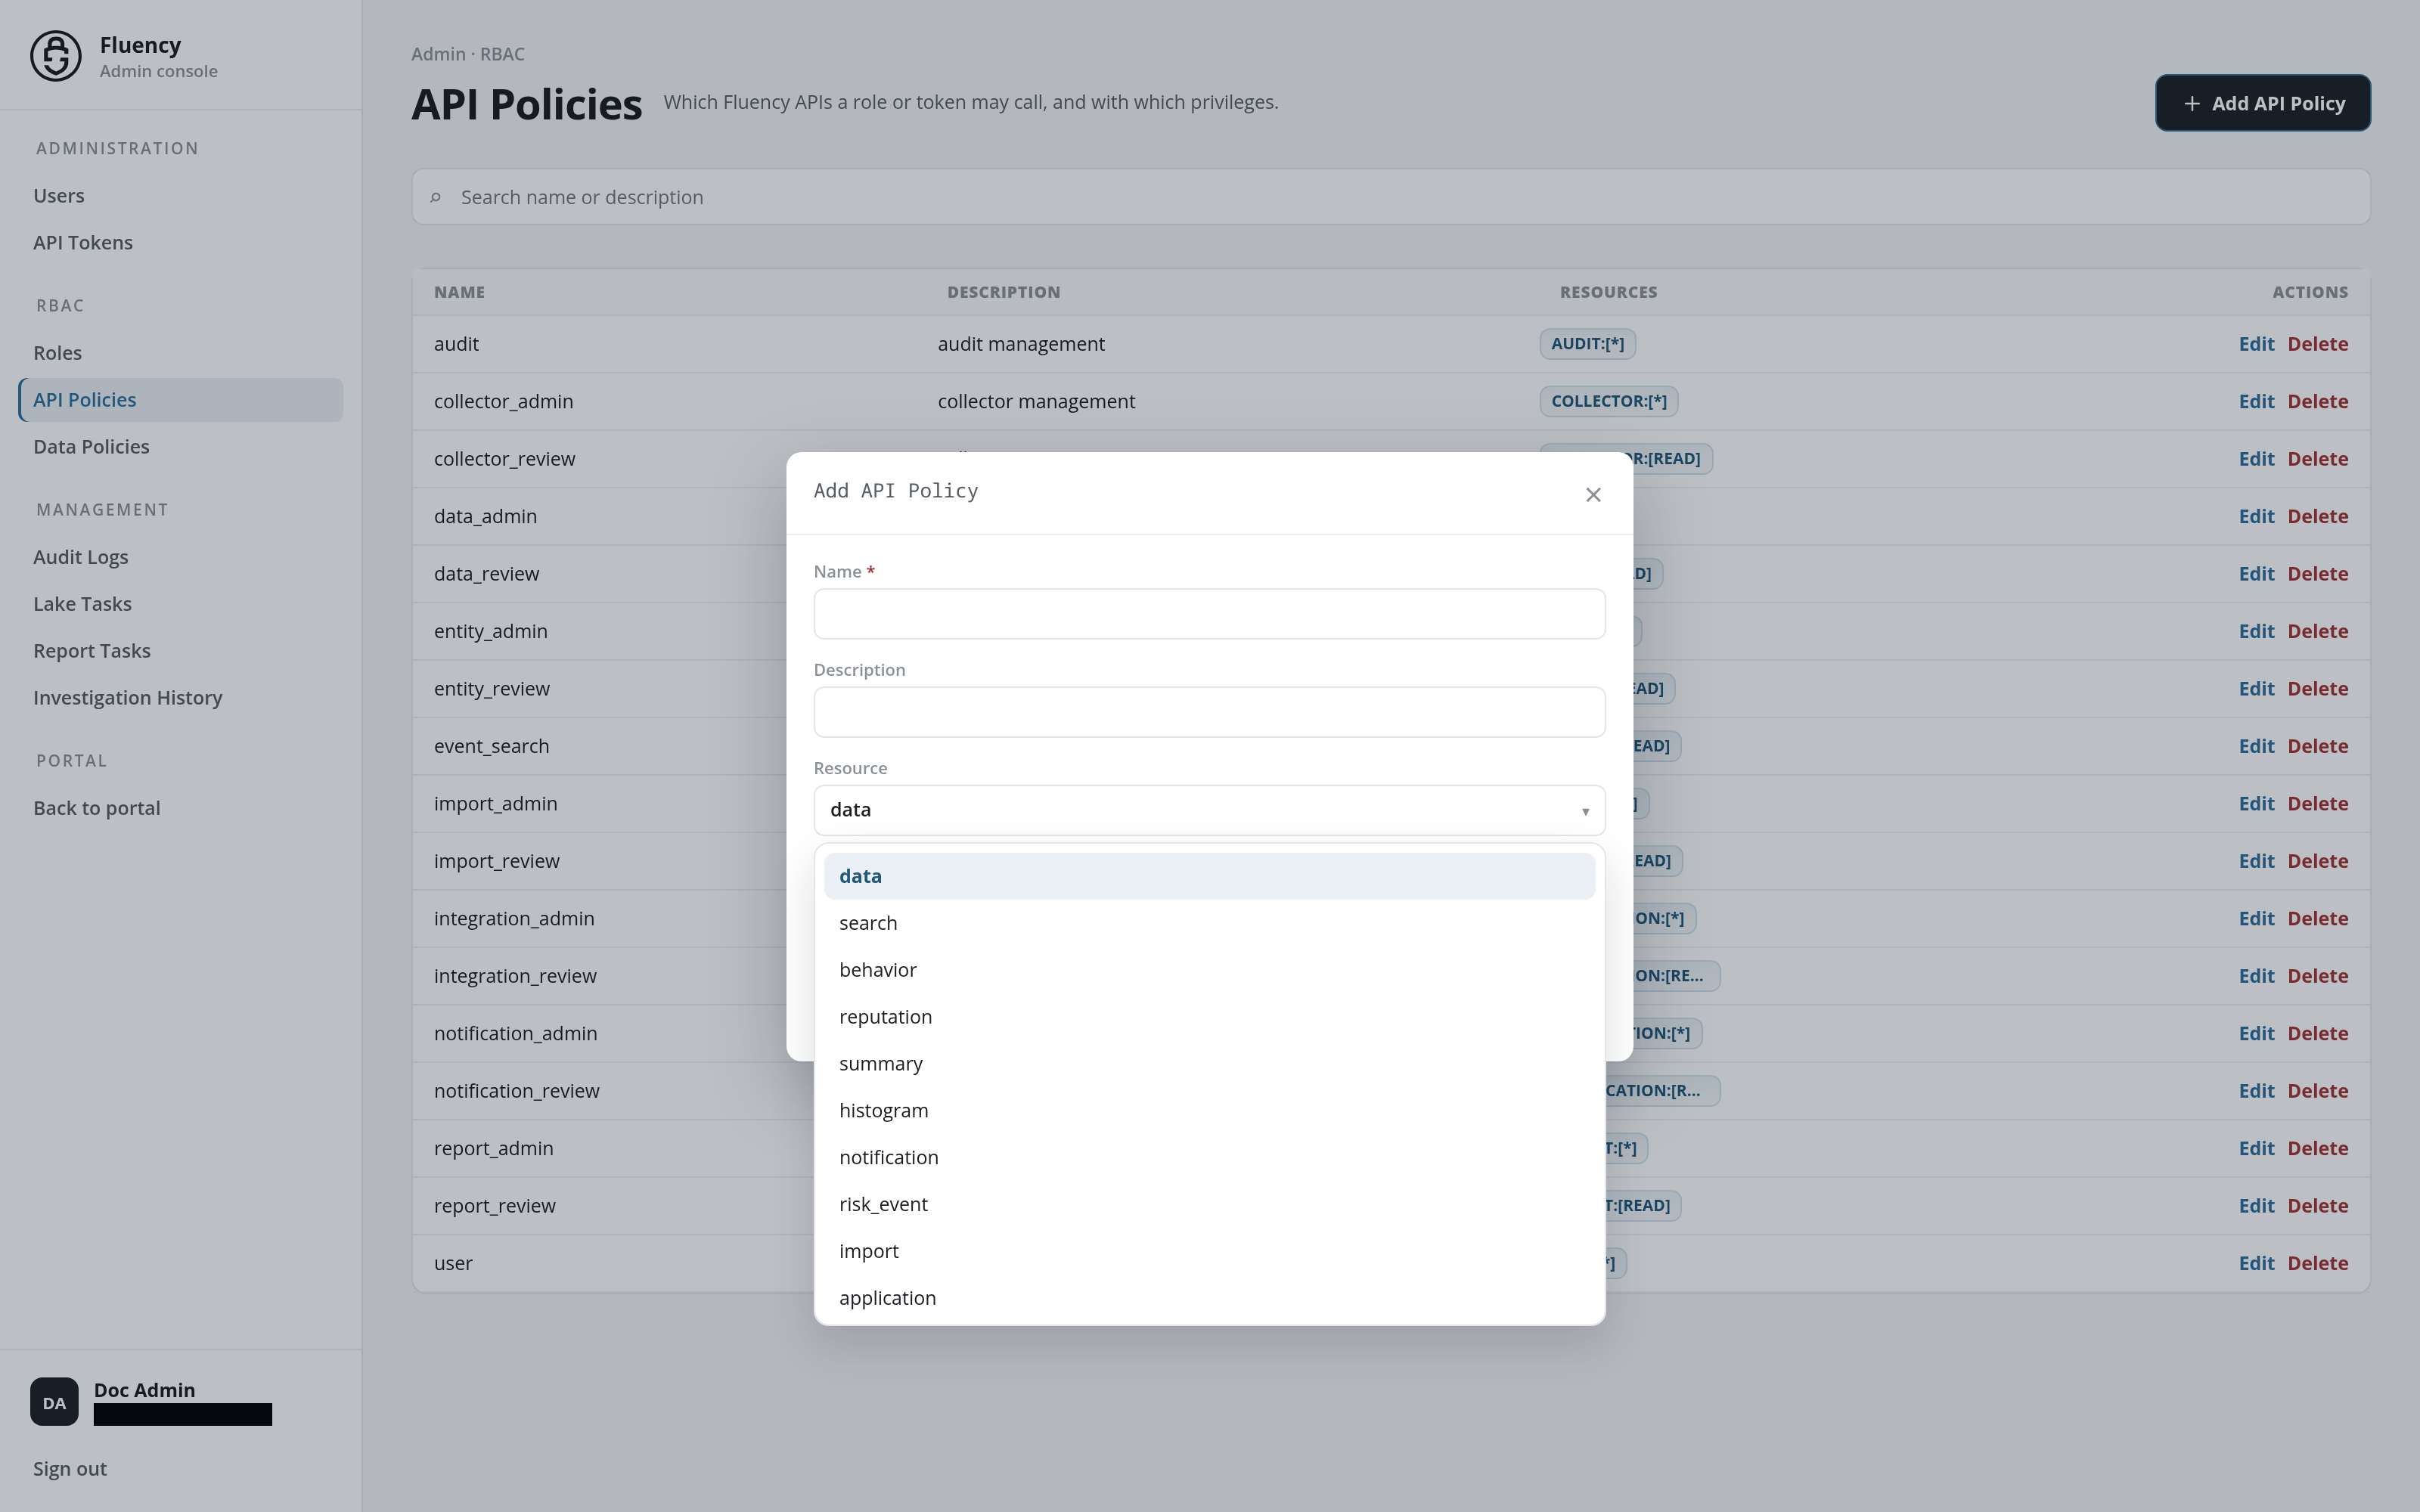
- Resource: a drop-down of the API resources a policy can cover; it starts on
data. - Privileges: a multi-select picker showing Add….
The Resource list offers data, search, behavior, reputation, summary, histogram, notification, risk_event, import, application, asset, integration, report, collector, audit, user, oauth, tenant, and grid. The current choice is highlighted.
The Privileges list offers read, create, update, delete, and *, which stands for every privilege.
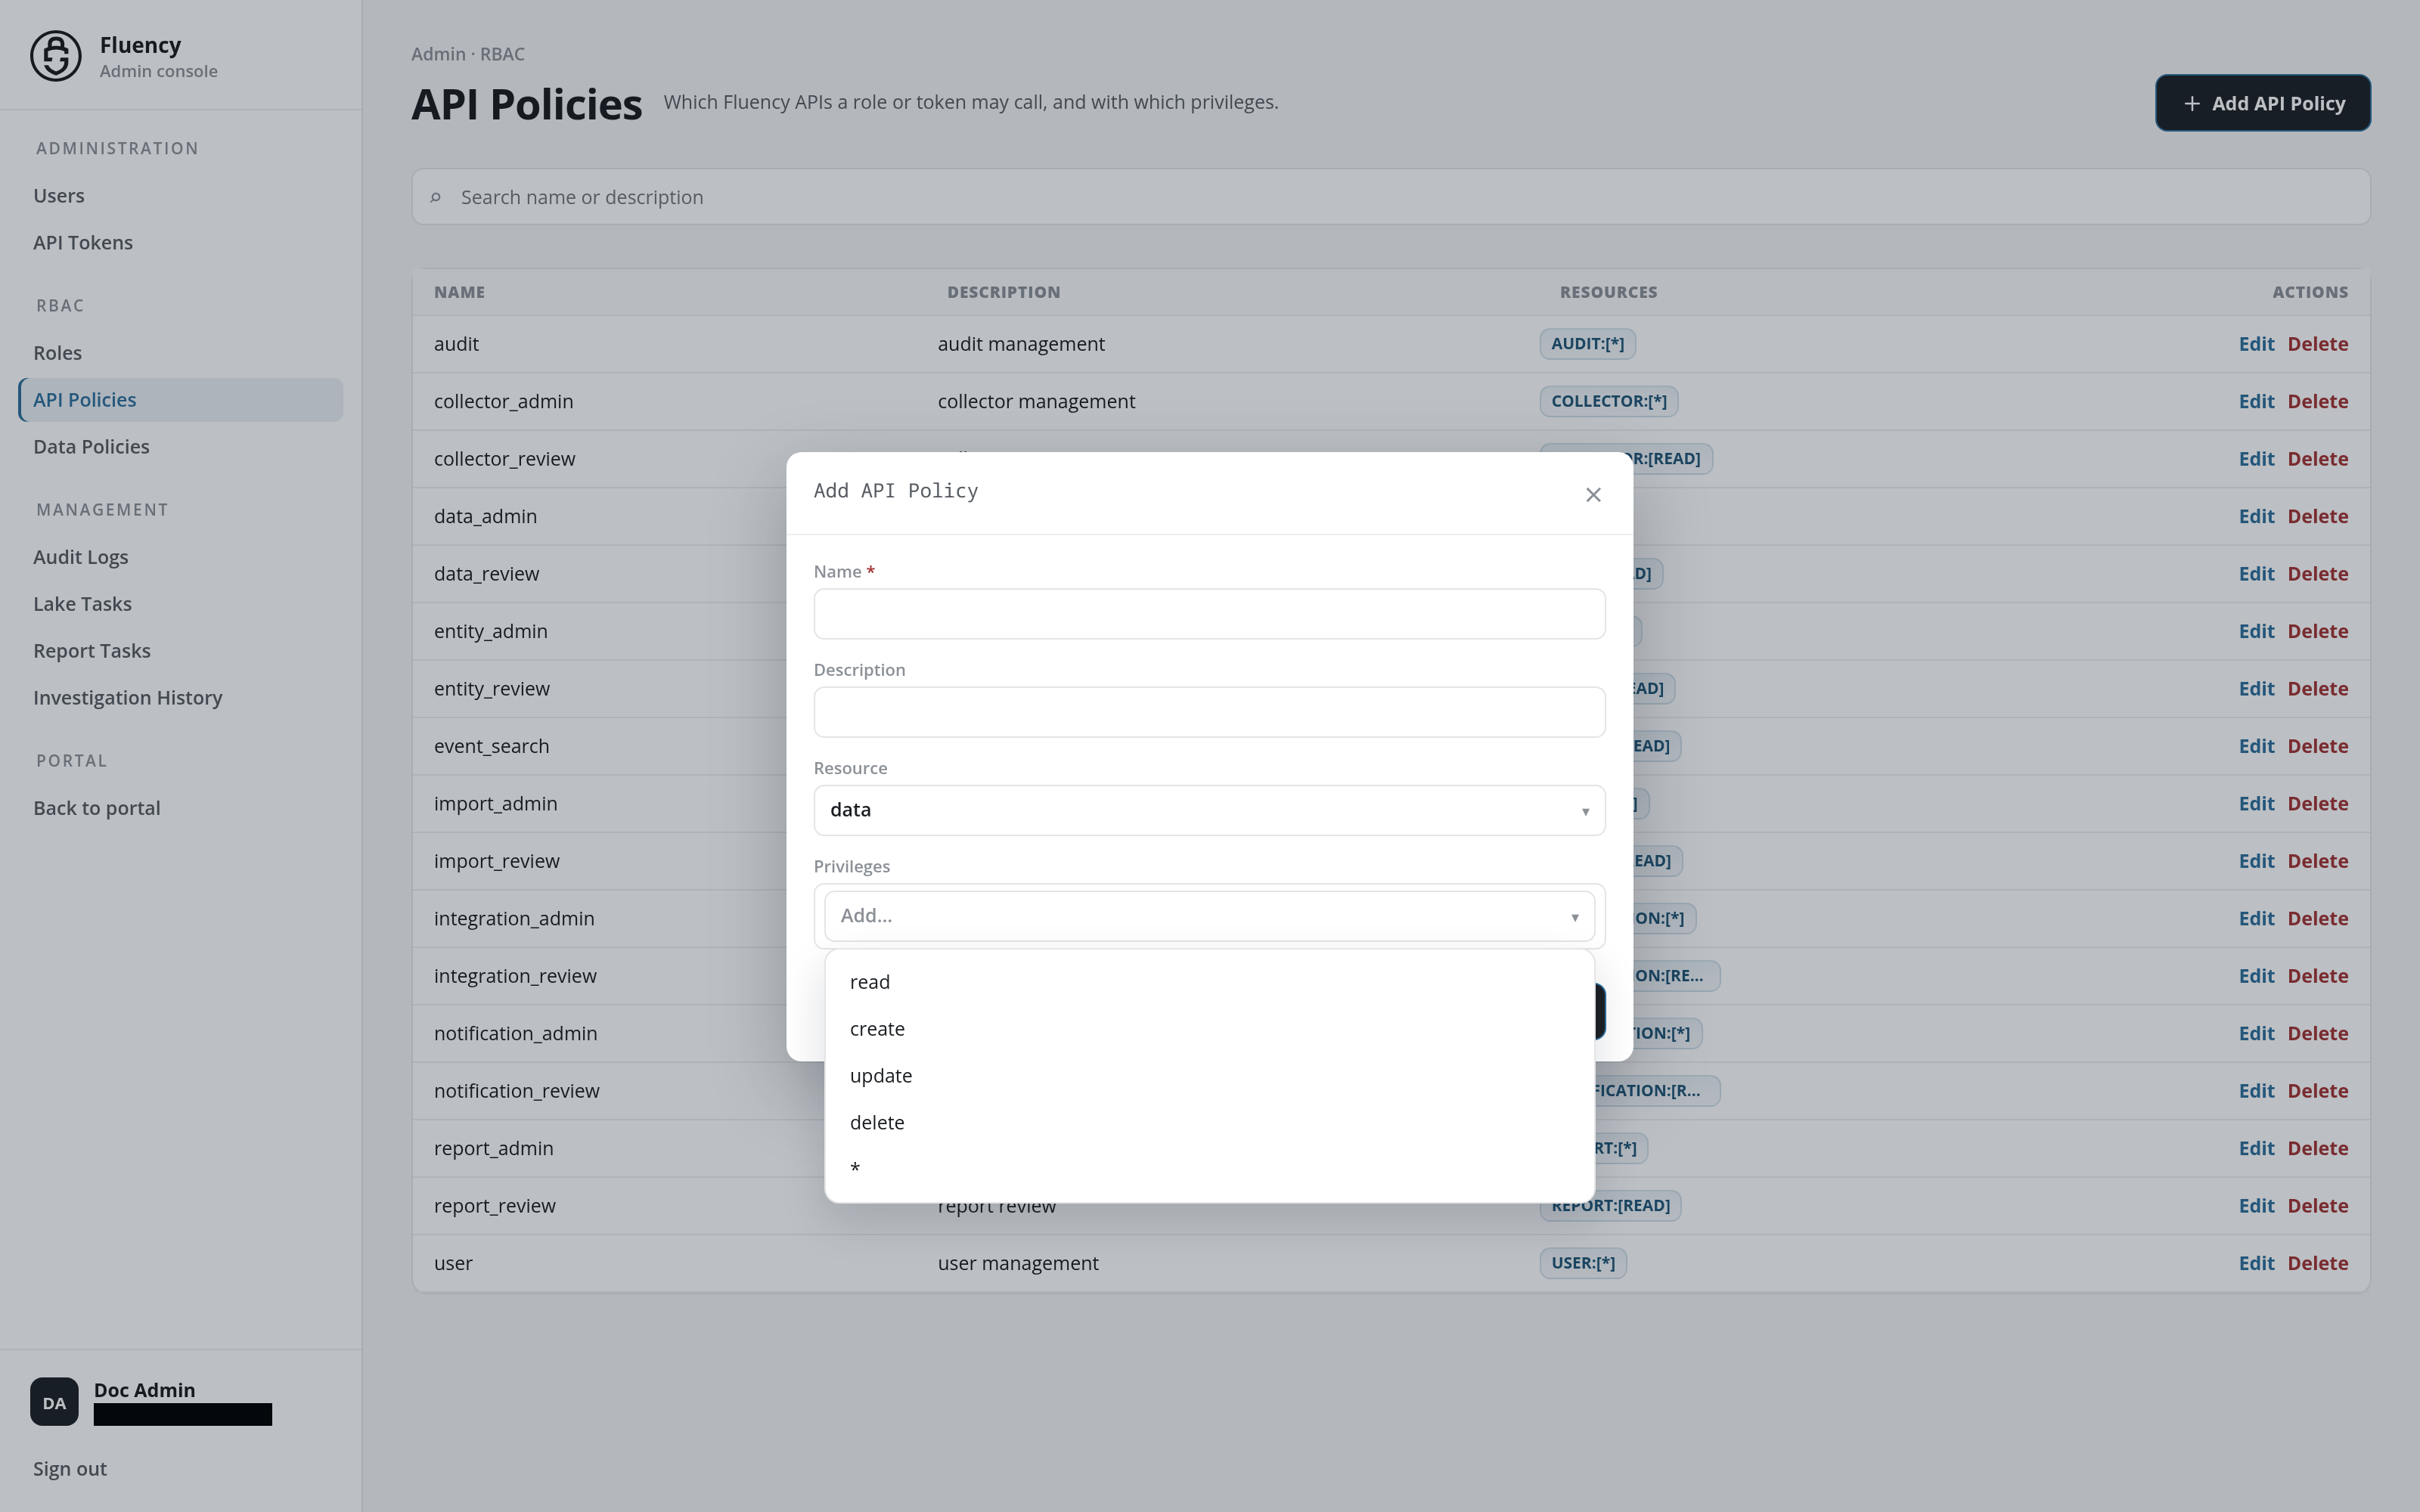
Each privilege picked is added above the picker as a chip with an × that removes it again.
Click Add to create the policy, or Cancel (or the × in the title bar) to close the dialog without saving. With Name empty, Add leaves the dialog open and the red band at the top of the page reads Name is required.
A policy covers one resource. When it is added, the dialog closes, the band reads API Policy added successfully., and the policy appears in the table with its resource and every privilege picked, such as BEHAVIOR:[READ, UPDATE]. It is then offered in the API Policies lists of Add Role and Add API Token.
Update API Policy
Click Edit on a row to open the Update API Policy dialog for that policy, with the same fields filled in from the policy and its privileges shown as chips.
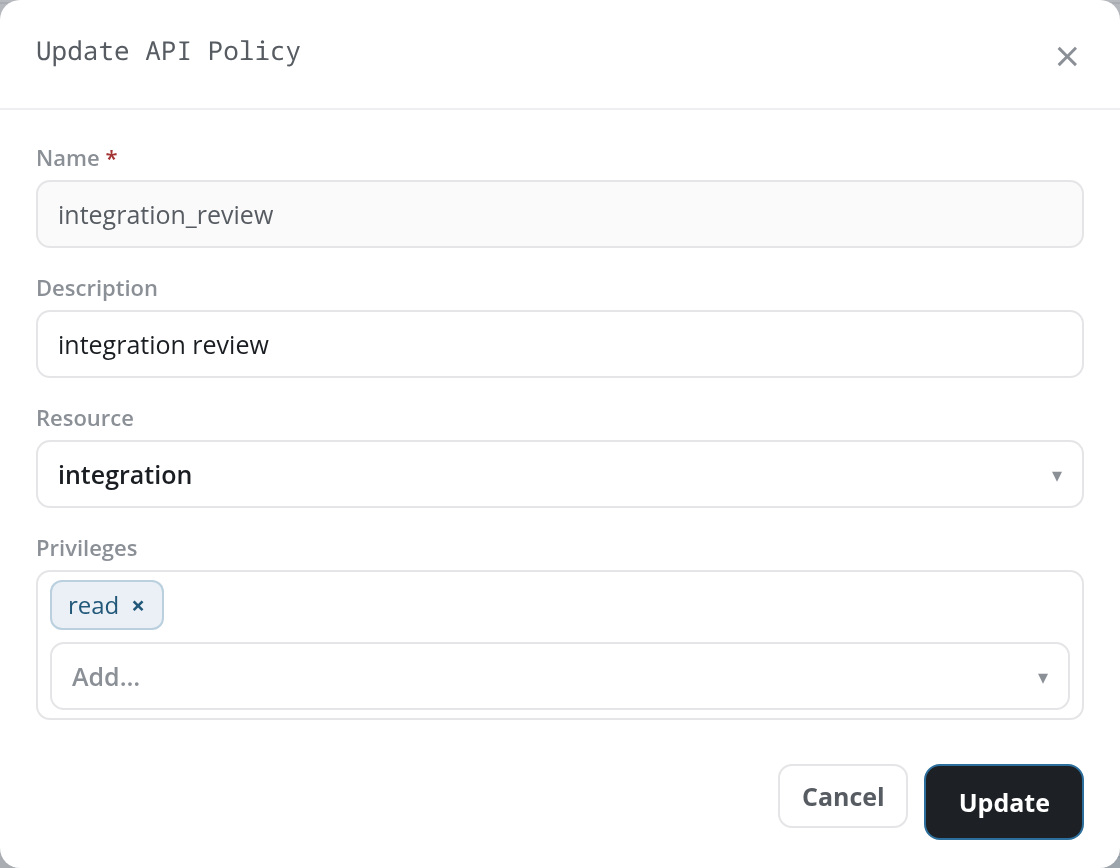
The Name field is read-only. Change the Description, pick another Resource, or add and remove privilege chips (a chip's × asks Delete followed by the privilege and This will remove it. Continue? first), then click Update to save, or Cancel to close the dialog without saving. A saved change reports API Policy updated successfully.
Delete an API Policy
A row's Delete action deletes the policy. A confirmation titled Delete API Policy asks Are you sure you want to delete followed by the policy's name; accept it to delete the policy, or cancel to keep it. A deleted policy leaves the table, and the band at the top of the page reads API Policy deleted successfully.