Notable Events
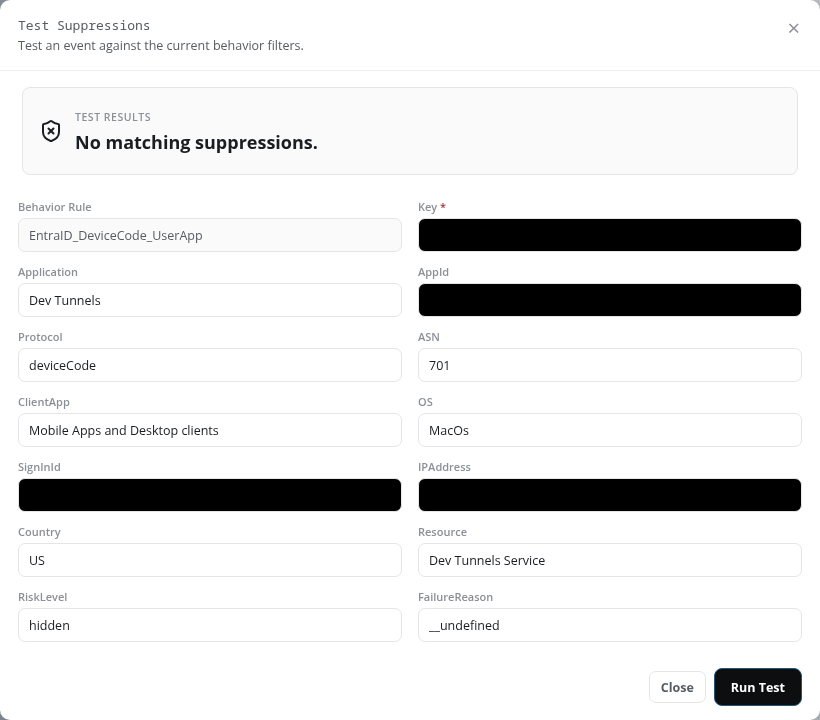
The Notable Events page is a faceted search across the account's notable behavior events. Type a search, pick a time range, and narrow the results with the filters on the left; the table on the right lists the matching events.
Menu path: Notable Events · URL path: /v2/notable-events
Page Layout
The header shows the breadcrumb Workspace / Search, the title Notable Events and the subtitle Faceted search across notable behavior events. Below it:
- Search bar: the search field, the time-range buttons, and Search.
- Result bar: the record count on the left, JSON line and ⚙ Columns on the right, followed by the filter chips once a filter value is chosen.
- Risk score chart: when the search has results, a RISK SCORE OVER TIME chart (n events plotted) across the full width, as on Cases Search.
- Filters panel (left): facet groups for narrowing the results.
- Results table (right): the matching events.
The page works the same way as Cases Search; what differs is the time ranges, the facets and the columns.
Search Bar
- Search field: free text matched across all fields (Search across all fields – an IP, a user, a behavior rule…).
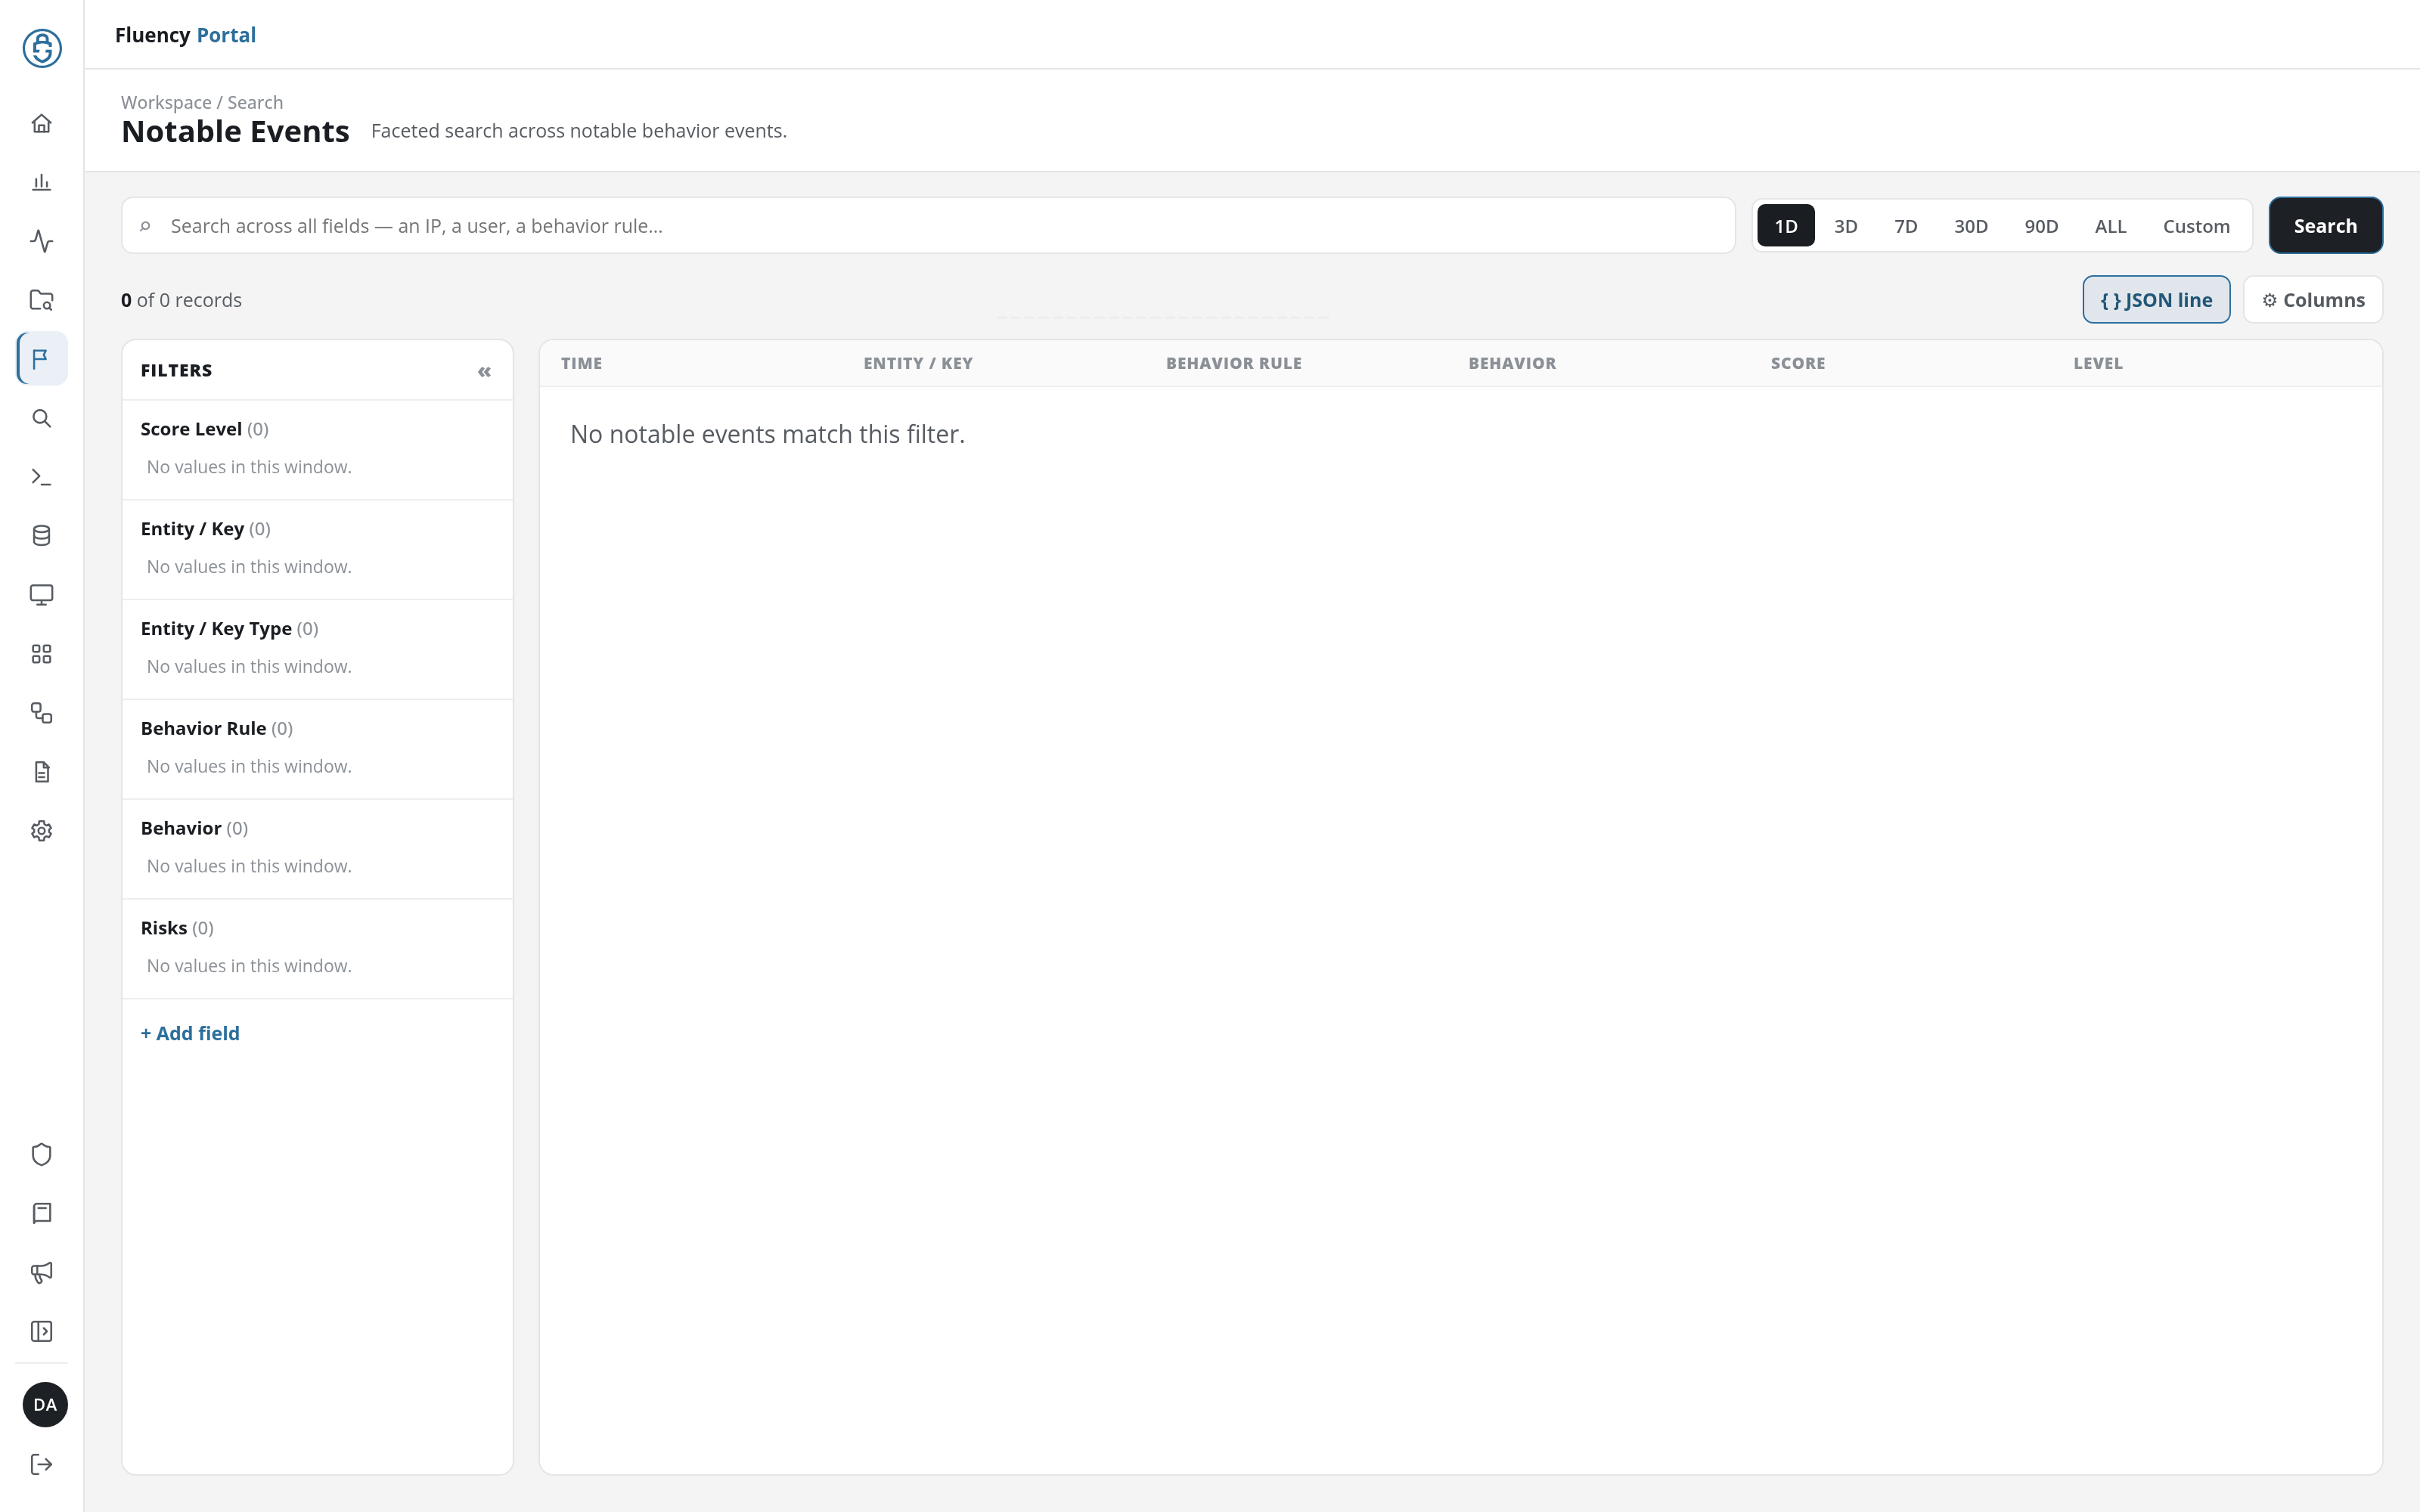
- Time range: 1D, 3D, 7D, 30D, 90D, ALL and Custom. The selected range is filled in black; the page opens on 1D.
- Search: runs the search with the current text, range and filters.
Click Custom to pick the dates yourself: two date fields, Start date (UTC) and, after the arrow, End date (UTC), appear between the range buttons and Search.
Result Bar
- Record count: N of M records: the events shown out of those that match.
- JSON line: a toggle that adds each event's JSON, on one line, below its row in the table, highlighted while on. It is on when the page is first opened in a browser; the browser remembers the choice, which applies to Cases Search and Behavior Rules as well.
- ⚙ Columns: opens the column chooser.
Filters
The FILTERS panel holds one group per facet, each with the number of values found in the selected range after its name:
- Score Level
- Entity / Key
- Entity / Key Type
- Behavior Rule
- Behavior
- Risks
A group with nothing to offer in the range reads No values in this window. + Add field at the bottom of the panel adds a facet group for another field, chosen from a Filter fields… list of the fields found in the results (the attribute names of the loaded events, such as Application, Country, or IPAddress); see Add Field on Cases Search. The new group is headed with the field's name, its number of values, and from loaded page, with an × that removes it.
The « button in the panel's upper-right corner collapses the panel to a narrow strip labelled FILTERS, giving the table the full width; the strip's » button opens the panel again.
Clicking a value works as on Cases Search (see Selecting Values): the first click includes it (✓, with a chip such as Score Level: <1000 × and Clear all), the second excludes it (−, NOT), and the third drops it. The search, range and filters are kept in the URL in the same way: q= for the search text, range=3D, 7D, 30D, 90D or ALL (the default 1D adds nothing), from=…&to=… for Custom, must= / not= for the chosen values, and field= for each group added with + Add field.
Columns
⚙ Columns opens a checklist of the columns the results table can show. Tick or untick an entry to add or remove that column.
| Column | Shown by default |
|---|---|
| Time | Yes |
| Entity / Key | Yes |
| Behavior Rule | Yes |
| Behavior | Yes |
| Key Type | No |
| Score | Yes |
| Level | Yes |
| Score Level | No |
| Risks | No |
| Customer | No |
Results Table
The table lists the matching events in the chosen columns; events with a risk score of zero are not listed. When nothing matches, it reads No notable events match this filter. Click an event to open its detail panel.
Event Detail Panel
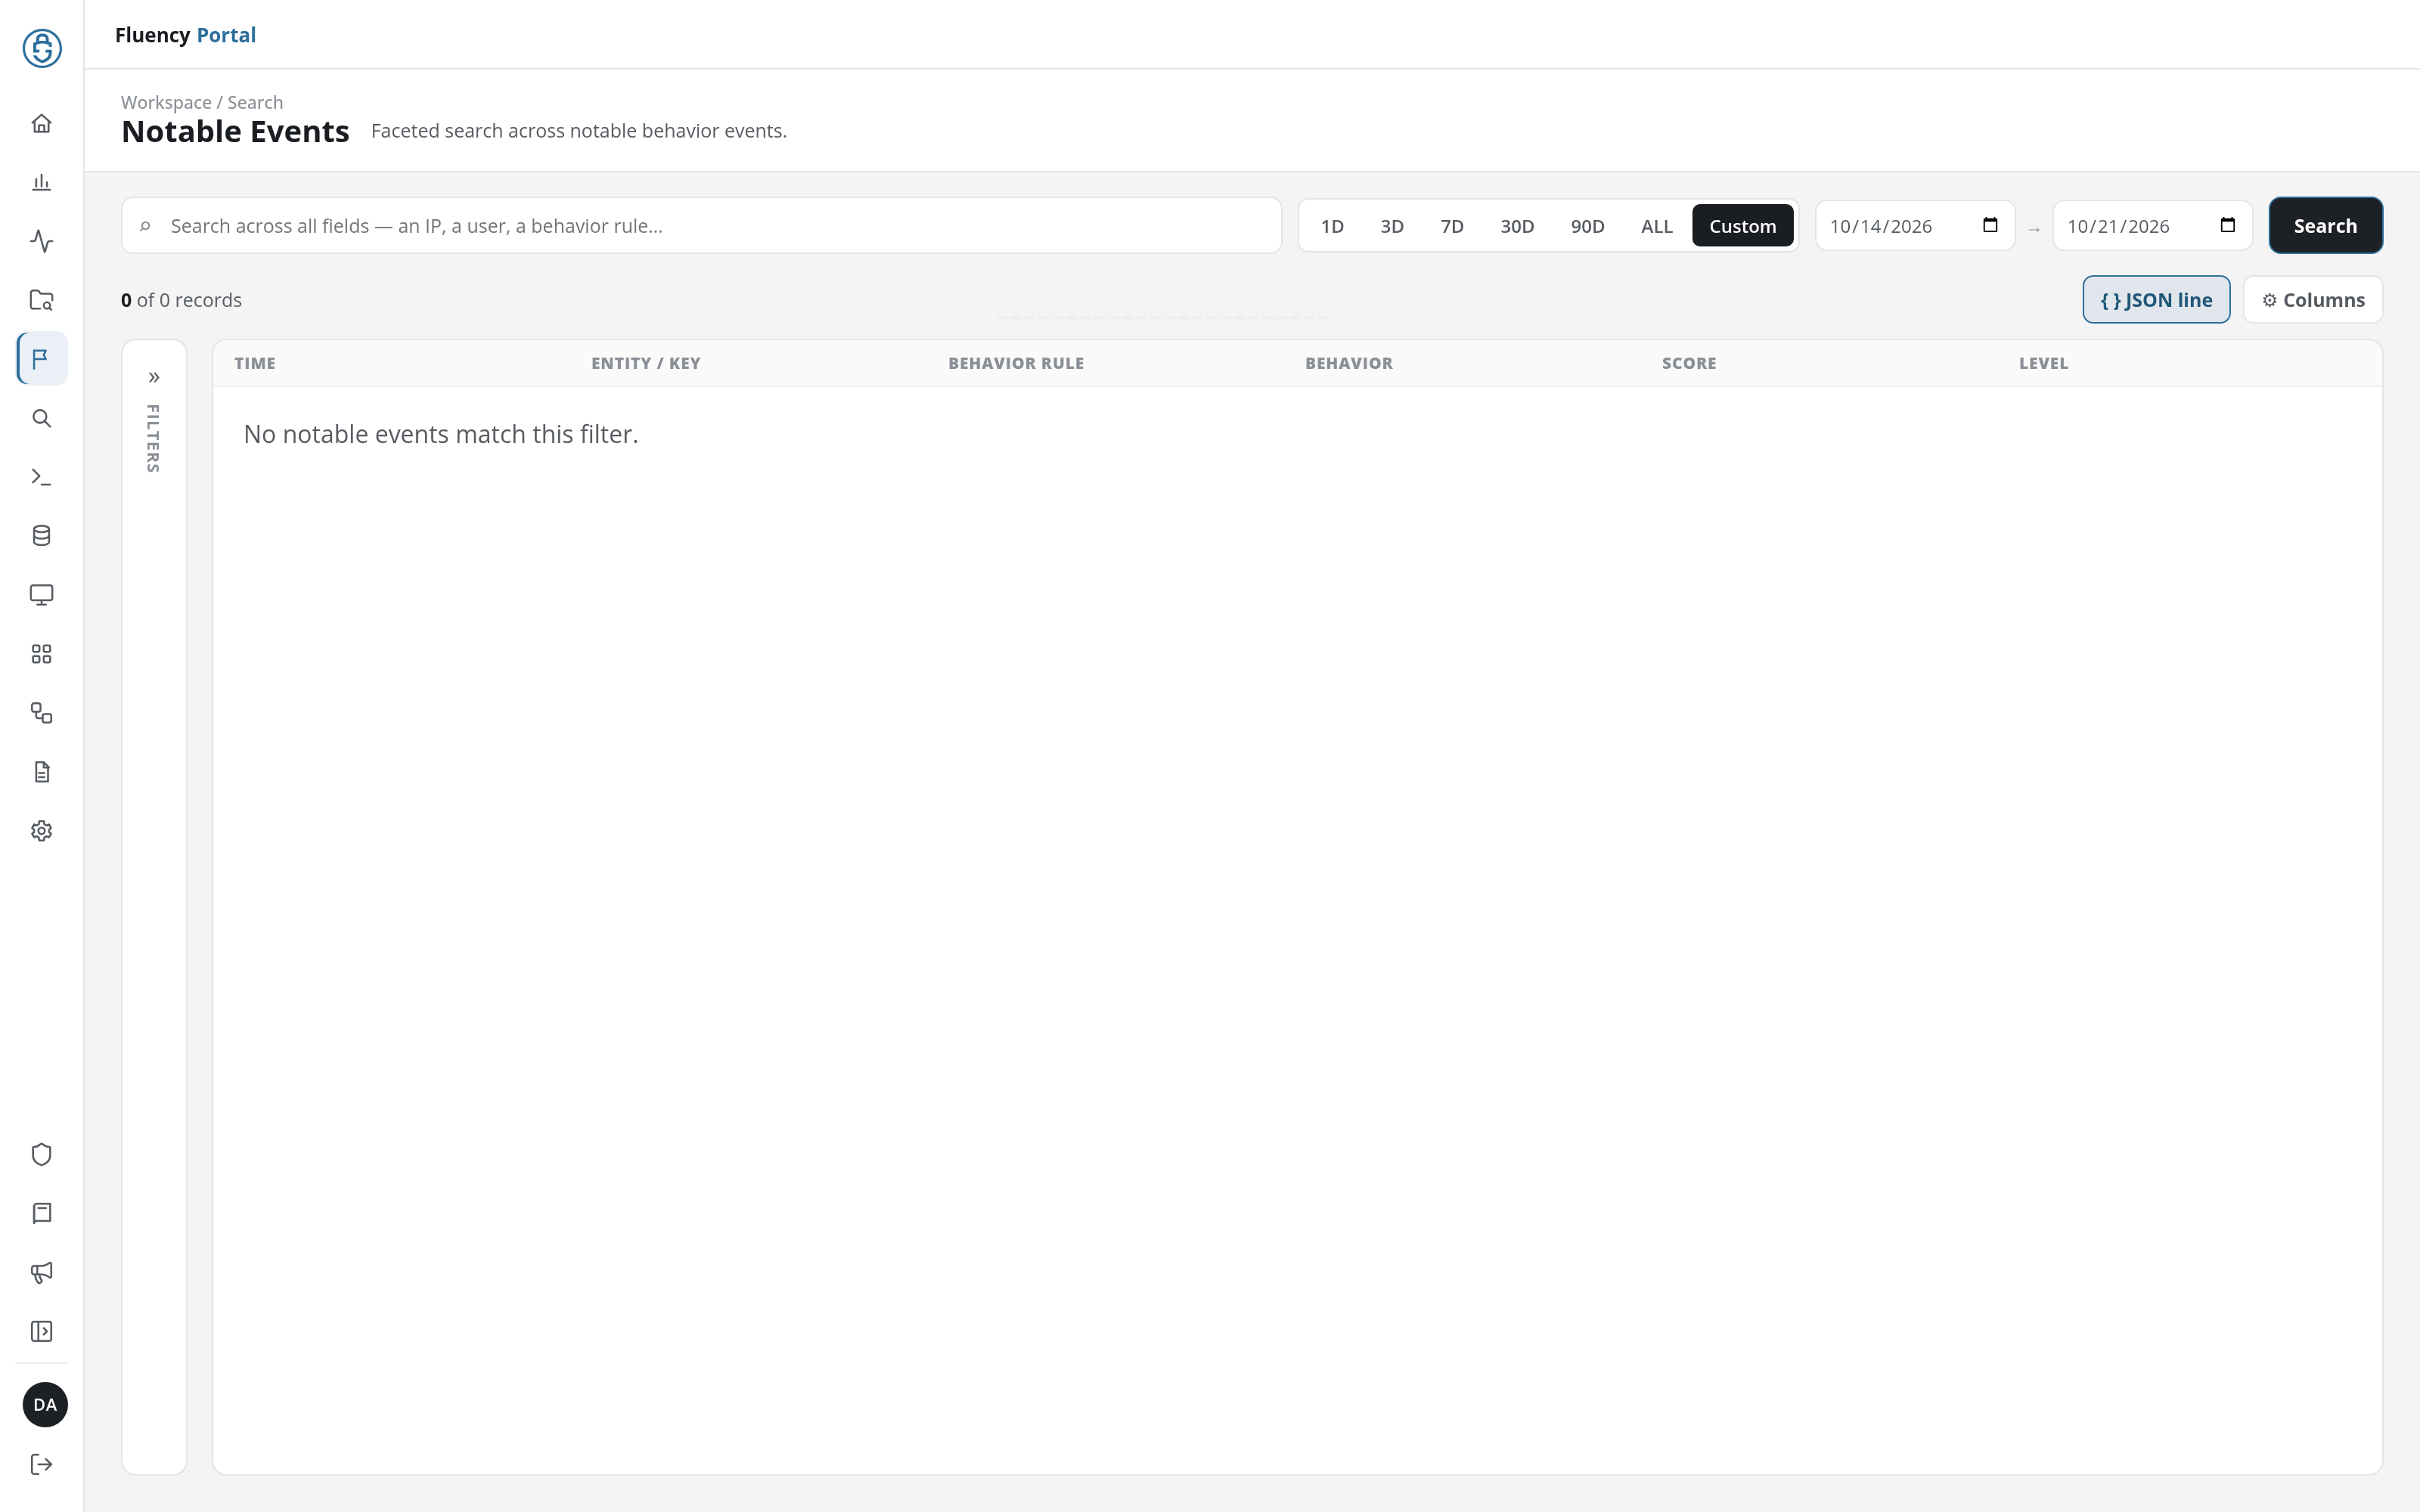
The panel slides in over the right of the page. Its header gives the event's entity, with the behavior rule beneath it, and the event's severity as a badge, with the × that closes the panel. Below:
- Test Suppressions: opens the Test Suppressions dialog for the event.
- OVERVIEW: Entity / Key, Key Type, Behavior, Behavior Rule, Time, Risk Score (with its severity badge), Score Level, and UUID.
- ATTRIBUTES: the fields the rule recorded, each with its alias, its value, and beneath the value the event field it came from (such as
@azure.properties.appDisplayName). - RAW JSON: the event's JSON record, collapsed, with Show and a copy button (Copy JSON).
Test Suppressions
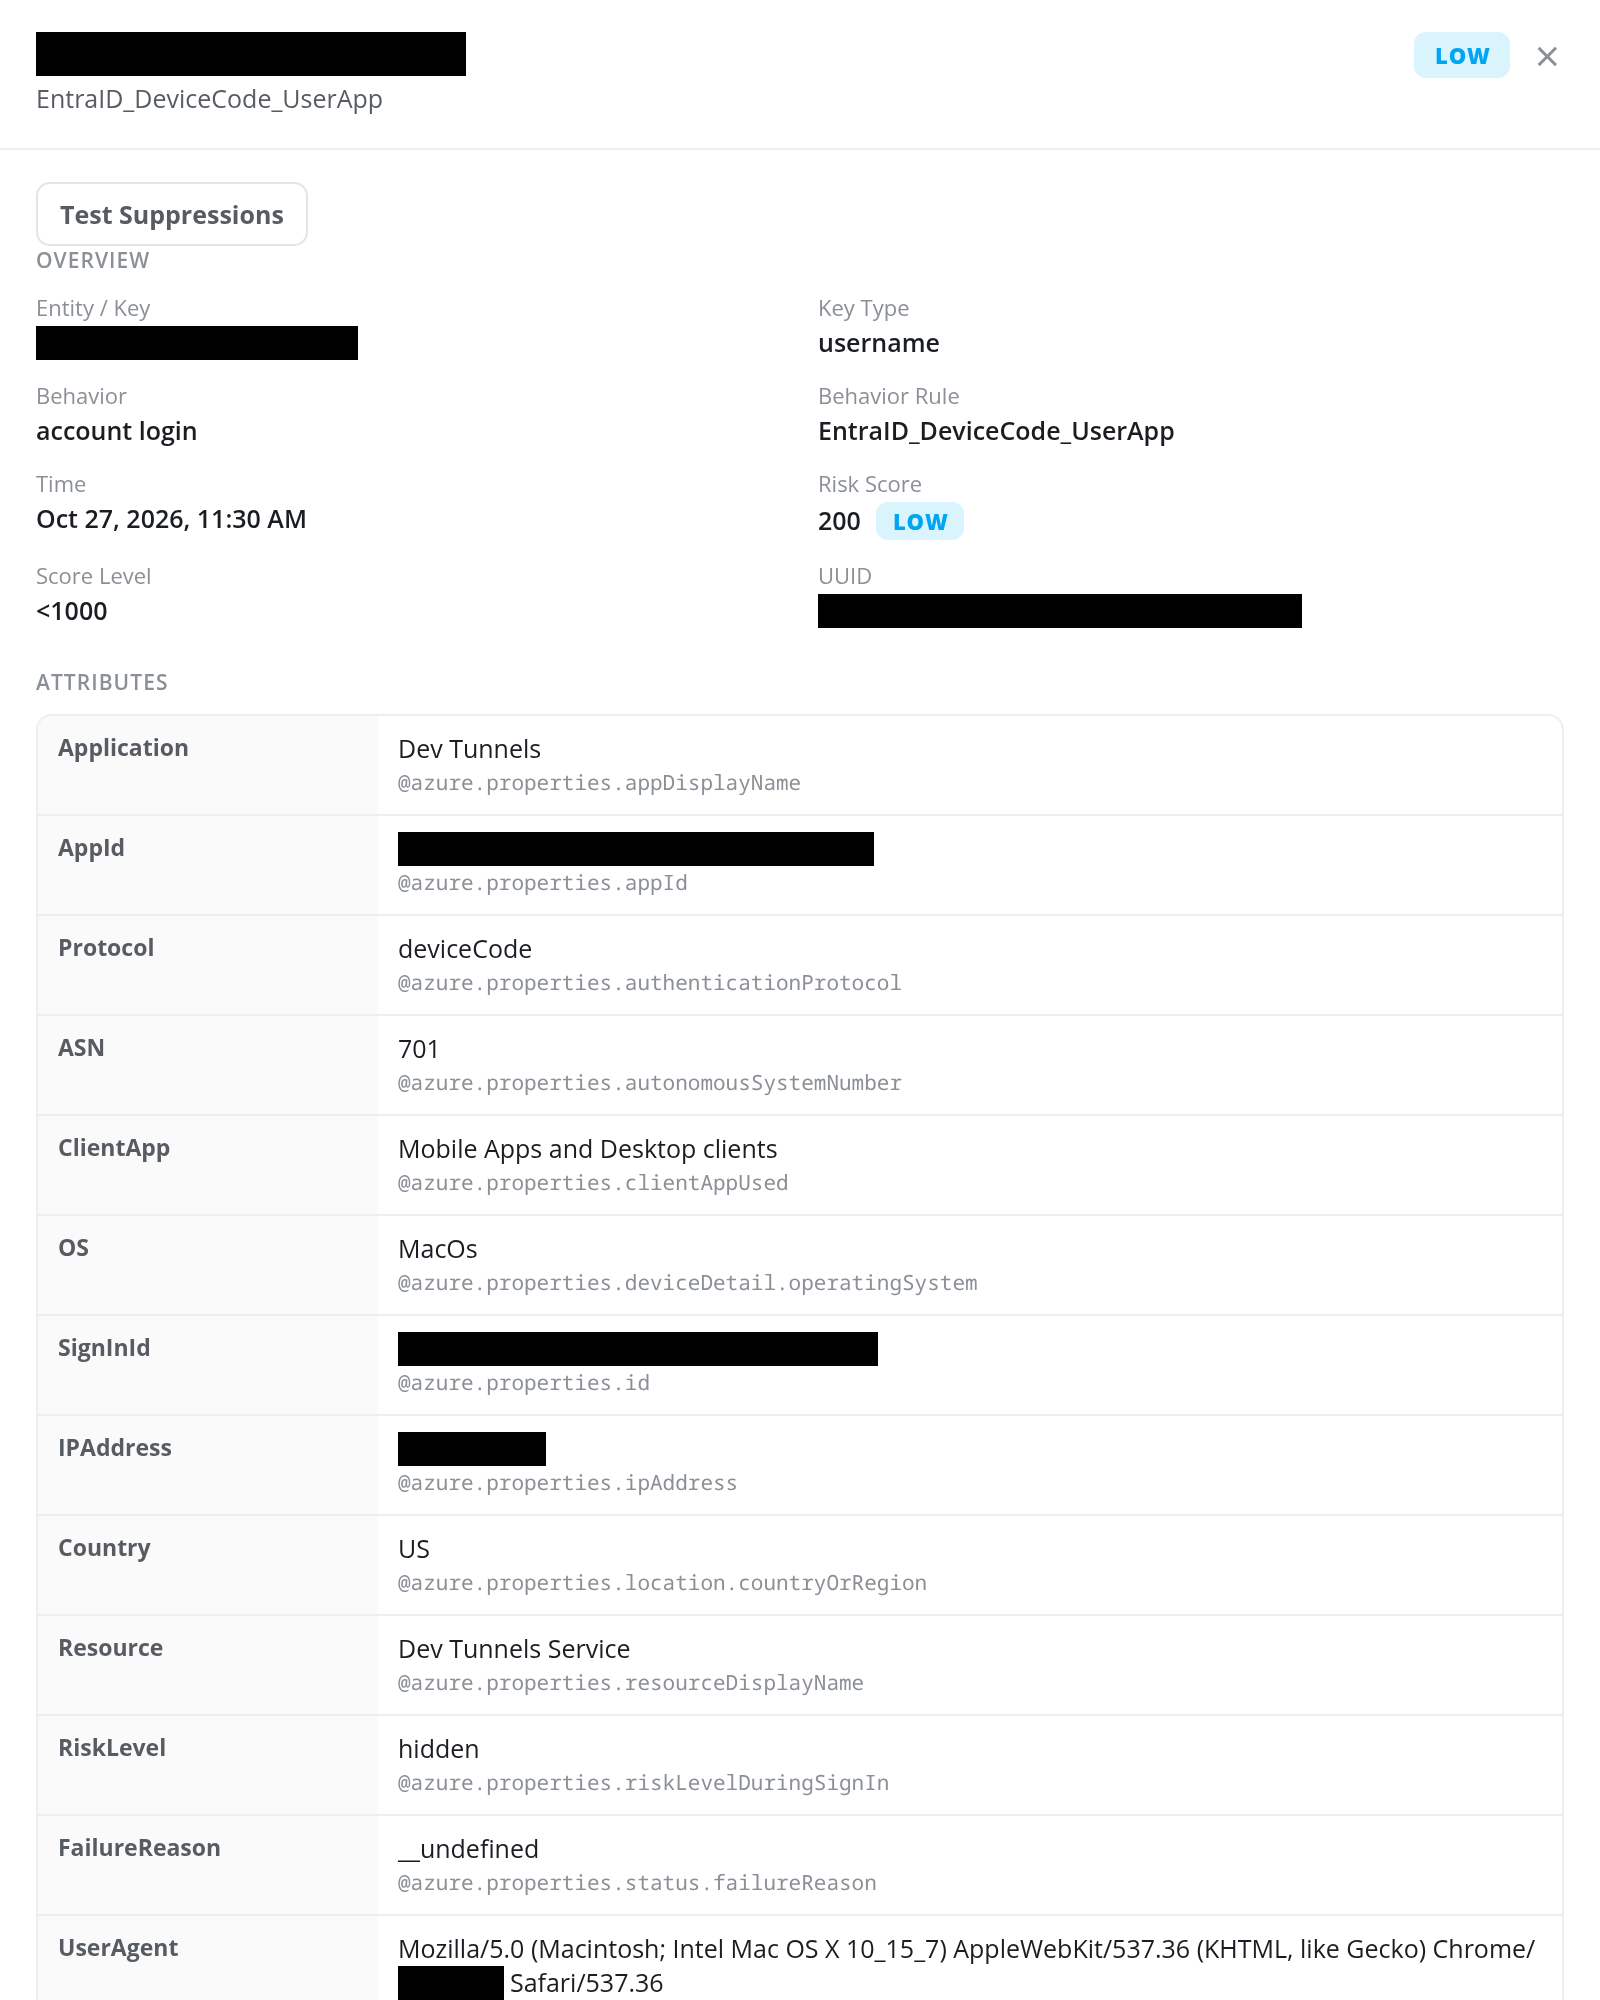
Test Suppressions opens a dialog of the same name, Test an event against the current behavior filters., which checks whether any behavior filter would suppress the event. It holds the Behavior Rule (read-only), the Key (required), and one field per attribute, each filled with the event's value and editable, so another variant of the event can be tested.
Run Test shows the outcome in a TEST RESULTS box at the top of the dialog: No matching suppressions. when no behavior filter matches. With Key empty, the box reads Suppression test failed with Key is required. Close closes the dialog.