Sophos UTM
Sophos UTM 9 — the appliance line that originated as Astaro Security Gateway — is the older Sophos unified threat management platform, still in service in many environments alongside or ahead of a migration to Sophos Firewall. It bundles packet filtering, web and mail protection, intrusion prevention, and site-to-site and remote-access VPN into one appliance, and it writes a separate log stream for each of those subsystems. Its packet-filter log in particular is a well-structured key-value format that records the interface, addresses, ports and the rule that made each decision.
Device-side setup
Configure the device to forward syslog to the listener described below, following the vendor's own documentation for its syslog export. Nothing has to be built on the platform side beyond installing the template below — it supplies the parser and wires the pipeline.
Syslog configuration
The appliance sends to a syslog listener: either the cloud syslog endpoint or a local collector appliance. The two destinations use different ports. The cloud endpoint has a per-tenant domain and a block of ports allocated to your account: Platform → Administration → Syslog Ports shows the domain, the port range, and which protocol listens on which port — read the numbers off that page rather than assuming a standard one. A collector appliance listens by default on UDP/514, TCP/514, TLS on 6514 and TLS RFC 6587 on 7514, and each of its listeners can carry a Customer Tag that attributes the records arriving on it. See Syslog Import for the protocol options and Syslog Ports for the listener configuration. Either TLS listener presents a certificate the sending device has to trust: the Download CA (ca.crt) button on the Syslog Ports page supplies it, and without it the handshake fails with nothing logged on the platform side.
Install the Application
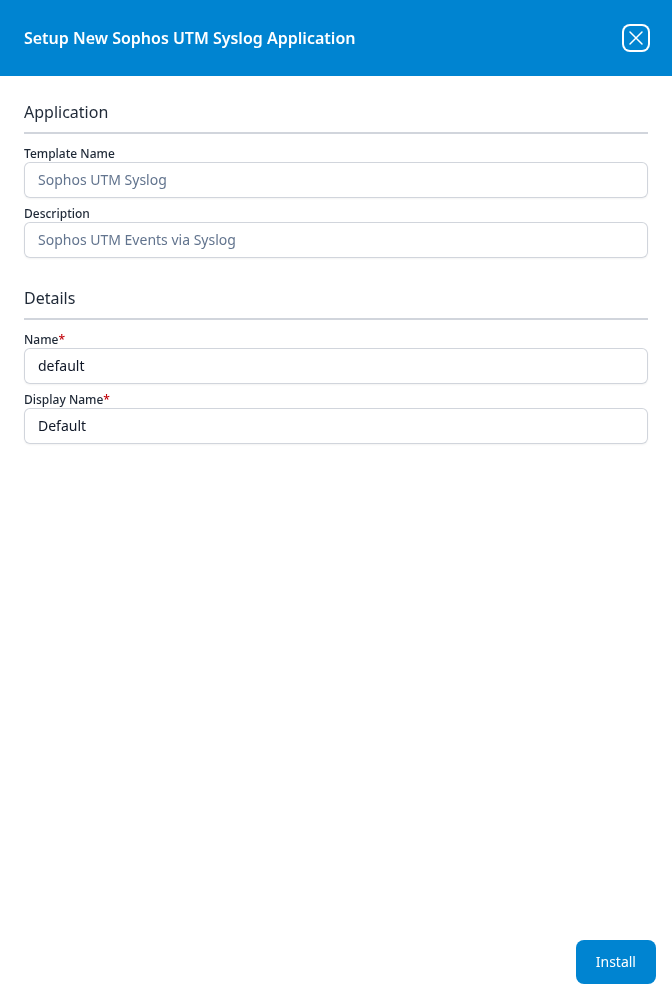
Go to Platform → Applications → Install Application From Template and choose Sophos UTM Syslog from the On-Premise IT category, then press Install. The template takes no parameters: it supplies the parser and builds the pipeline, and the transport is configured on the syslog listener rather than on the form. There is no source to add, no processor to attach, and no sink to wire by hand.
Related
- On-Prem / Syslog — other syslog devices.
- Sophos UTM parser — the FPL parser cookbook for this appliance's syslog. The template ships a parser already, so this is only needed if you want to customise the parsing.
- Sophos Firewall — the current Sophos network product, with a different log format.
- Syslog Import and Syslog Ports — the transport and listener.